The Department of Information and Communications Technology (DICT) said on Friday, Sept. 25, that it is investigating a possible exposure of 410 files associated with 48 companies in its Trusted Assessment Provider (D-TAP) accreditation program.
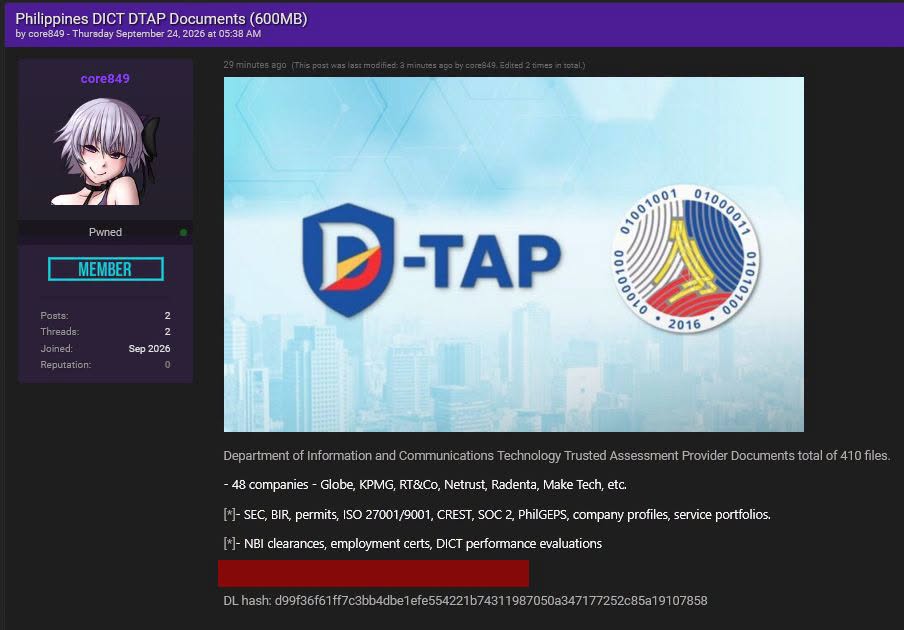
Cybersecurity news site Deep Web Konek reported that a threat actor using the alias “core849” posted a claim on Sept. 24 that the files had been leaked.
The collection was described as roughly 600 MB, or 770 MB uncompressed. The authenticity of the files and how they were obtained have yet to be established.
“The Department of Information and Communications Technology (DICT) acknowledges the report of a possible data exposure involving a DICT Trusted Assessment Provider (DTAP). The incident is currently being handled by the National Computer Emergency Response Team (NCERT) under the DICT Cybersecurity Bureau,” the agency said in a statement.
According to DICT, the reported files may include corporate registration records, permits, certifications, cybersecurity credentials, employment documents, and performance evaluations.
Deep Web Konek also reported that the alleged collection includes documents linked to Globe, KPMG Philippines, Netrust, Radenta, and Make Technology. Their appearance in the reported collection does not establish that any of those companies’ systems were breached.
DICT said it is checking the documents’ authenticity, source, and extent of exposure. NCERT is coordinating with the D-TAP provider concerned and other parties to determine what happened.
“Should the investigation confirm that personal or other protected data has been compromised, DICT will take appropriate action, including notifying affected parties as applicable and in accordance with the Data Privacy Act of 2012 (Republic Act No. 10173), its implementing rules and regulations, and other relevant policies,” the agency said.
DICT has not identified the source of the reported files or confirmed whether its own systems were compromised.