The Department of Information and Communications Technology (DICT) confirmed on Friday, Oct. 2, that a website under development was defaced, prompting an assessment of the unauthorized access and a review of its security controls before deployment.
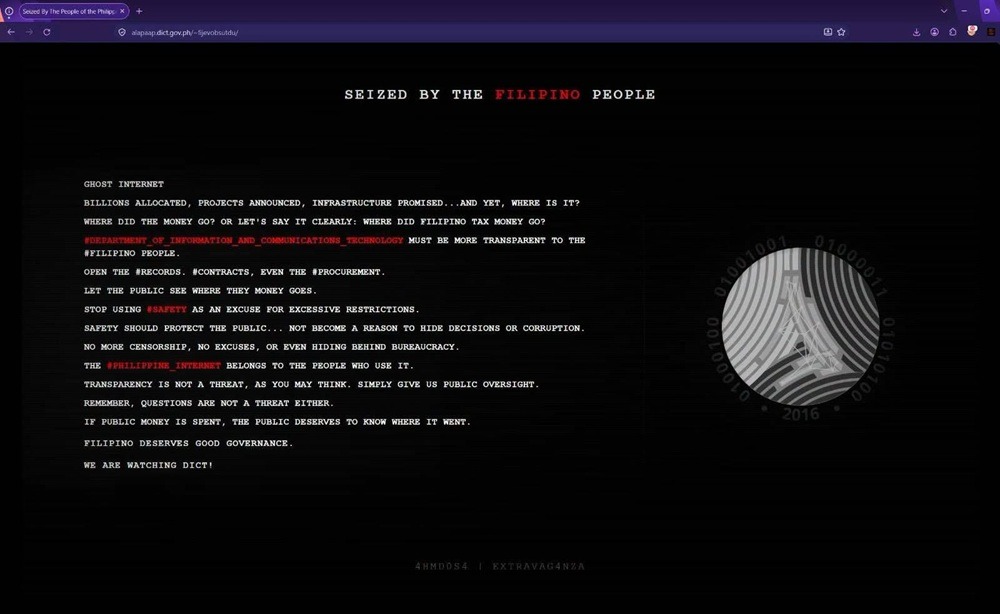
The department issued the statement after cybersecurity monitoring group Deep Web Konek reported that a threat actor using the name 4HMDOS4 had claimed responsibility for the incident.
According to Deep Web Konek, the defaced page carried a message criticizing government spending, transparency, procurement, and the use of “safety” to justify restrictions. It also called for greater public oversight of DICT.
The group said the unauthorized content was immediately taken down and was no longer visible on the affected page.
DICT said the incident involved a staging environment used to develop, test, and validate a website before its official deployment.
“The affected site was a development and testing environment and was not the final version of the website intended for official public implementation,” the department said.
The environment was being used to evaluate the website’s functionality, configurations, and other components ahead of deployment, according to DICT.
“Upon detection of the incident, DICT immediately initiated an assessment of the affected environment to establish the circumstances surrounding the unauthorized access and determine whether any security weaknesses may have been involved,” it said.
The department said it was reviewing the environment for vulnerabilities requiring remediation. The findings would guide corrective measures and improvements to security controls before the website proceeds to official deployment.
“As a precautionary measure, the Department will ensure that the necessary security checks and validation activities are completed before any related system is made available for official public use,” DICT said.
The statement did not identify the affected website, explain how the unauthorized access occurred, or confirm the identity of the party responsible. It also did not disclose whether any data had been accessed or whether other systems were affected.