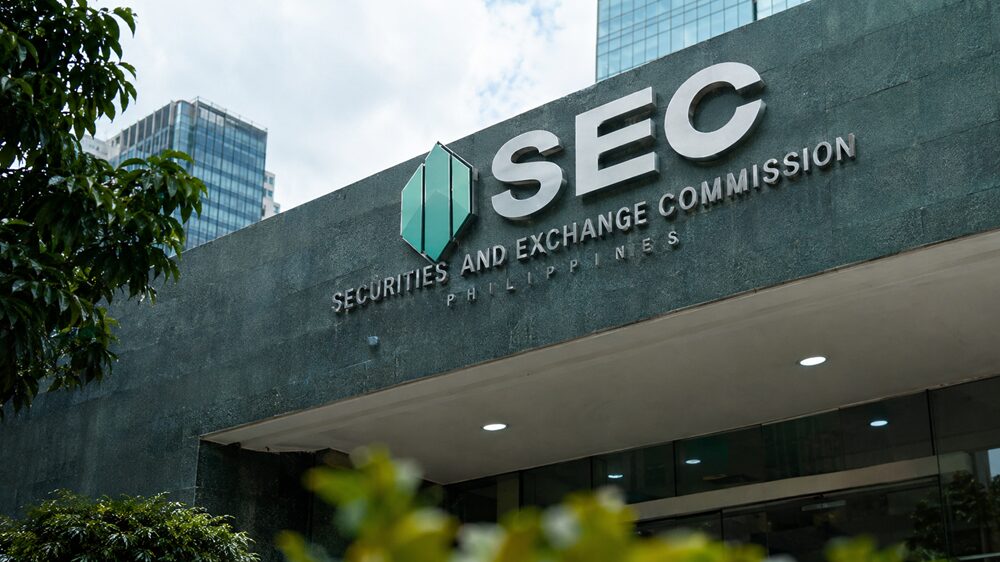
The Securities and Exchange Commission (SEC) has launched a system-wide security audit following a data security incident detected on Nov. 6, amid claims that approximately 487,000 lines of data associated with the agency have been posted on an online cybersecurity forum.
The incident came to public attention after a forum user operating under the alias “sinigangmixwithgabi” published a listing titled “Philippines Securities and Exchange Commission data 487K Lines” on Nov. 5, according to cybersecurity monitoring group Deep Web Konek.
The forum post allegedly offered a dataset containing approximately 487,000 lines of information linked to the SEC, along with a download link that would allow other users to retrieve the files.
The authenticity of the dataset, the number of individuals potentially affected, and the extent of any unauthorized access have yet to be independently established.
In a statement issued on Nov. 9, the SEC confirmed that it was investigating a data security incident detected on Nov. 6 and conducting a comprehensive audit of its digital platforms and databases.
Initial findings indicated that no company records were affected, no passwords were leaked, and no data had been modified or altered, the regulator said.
However, the SEC acknowledged that certain personal information may have been exposed.
“The categories of personal data that may have been exposed include individual profile information. The Commission is currently verifying the origin, scope, and validity of these affected records,” the SEC said.
The agency did not specify the number of individuals whose information may have been compromised or identify the particular systems involved.
It also did not confirm whether the alleged 487,000-line dataset circulating online was connected to the security incident it detected.
According to the SEC, its internal database infrastructure remains intact, and its preliminary investigation has found no evidence of unauthorized changes to corporate records.
Following the discovery, the regulator initiated containment measures, including security scans, digital forensic examinations, checks for indicators of compromise, and analyses of system logs to determine whether its infrastructure had been accessed without authorization.
The SEC also reinforced access controls, updated authentication credentials, and introduced additional monitoring rules and technical safeguards intended to prevent further security incidents.
The agency said it had implemented heightened monitoring to detect suspicious account activity across its online services, along with additional verification procedures for account-related requests and security updates.
The SEC formally notified the National Privacy Commission (NPC) of the incident on Nov. 9, in accordance with mandatory data breach reporting procedures.
The disclosure raised concerns over the security of personal information held by the SEC, which maintains corporate registration records, regulatory filings, and other information submitted by businesses, investors, and individuals dealing with the agency.
As a precaution, the SEC advised users of its online platforms to change passwords that are reused across multiple accounts, enable multifactor authentication, and avoid sharing login credentials, one-time passwords, or email verification links.
It also urged users to scan their devices for malware, monitor their accounts for suspicious activity, and exercise caution when receiving unexpected emails, calls, or text messages requesting personal information.
The investigation remains ongoing, with the regulator still determining the origin and extent of the possible data exposure.