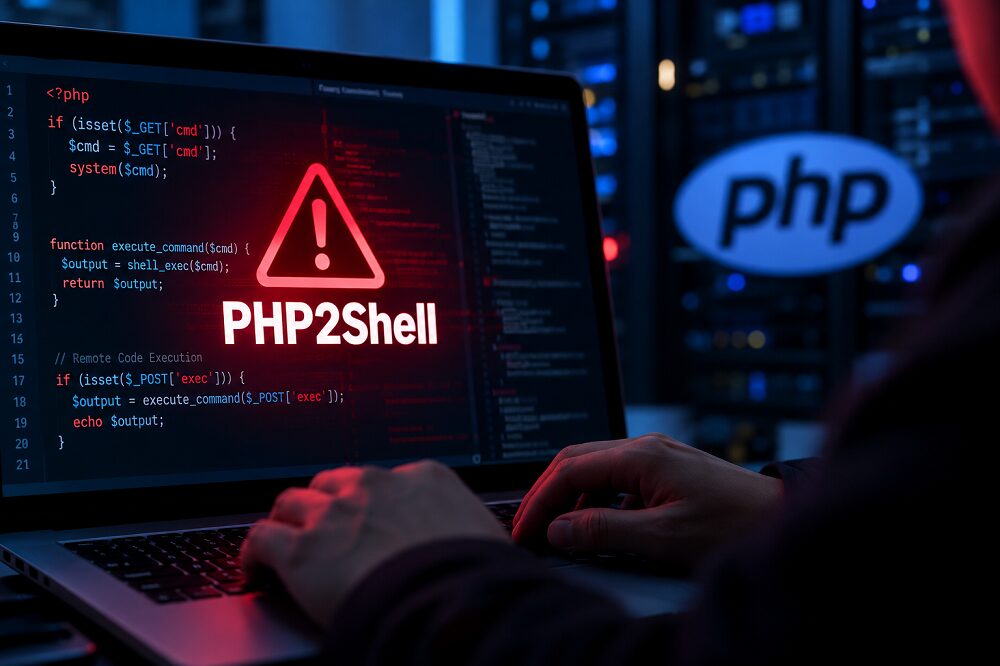
The National Computer Emergency Response Team (CERT-PH) has warned system administrators, Web developers, and hosting providers to patch two critical vulnerabilities in PHP that could allow attackers to remotely execute malicious code on affected servers.
CERT-PH is the official national cybersecurity incident response team under the Department of Information and Communications Technology (DICT).
In a cybersecurity advisory dated Oct. 22, 2026, CERT-PH identified the vulnerabilities, collectively known as PHP2Shell, as CVE-2026-109618 and CVE-2026-109619.
The agency urged organizations to review their PHP environments, determine whether their systems are vulnerable, and apply the appropriate security patches as soon as possible.
Remote code execution (RCE) vulnerabilities can allow attackers to run commands or malicious code on a target system.
Depending on the affected environment and the attacker’s access, exploitation could expose sensitive information, enable unauthorized changes to websites, or disrupt online services.
PHP is a server-side programming language widely used to build and operate websites and web applications. Vulnerable PHP installations may therefore expose public-facing websites and services to attacks.
CERT-PH stressed the importance of timely remediation, continuous monitoring, and prompt incident response to reduce potential threats and strengthen cybersecurity resilience.
System administrators and hosting providers should inventory their PHP installations, verify which systems are affected, and install the relevant security updates, the agency said.
Web developers should also check whether applications and hosting environments rely on vulnerable PHP versions, it added.
Organizations should monitor server and application logs for suspicious activity and investigate possible signs of unauthorized access or code execution, the agency said.
Where a compromise is suspected, PH-CERT said affected organizations should activate their incident-response procedures and take appropriate steps to contain the incident.
CERT-PH advised organizations to address vulnerabilities in underlying server software, rather than focusing only on application-level security.
The agency’s warning covers government and private-sector organizations that operate affected PHP environments.
However, the advisory information did not establish that any Philippine organization has been compromised through these vulnerabilities.