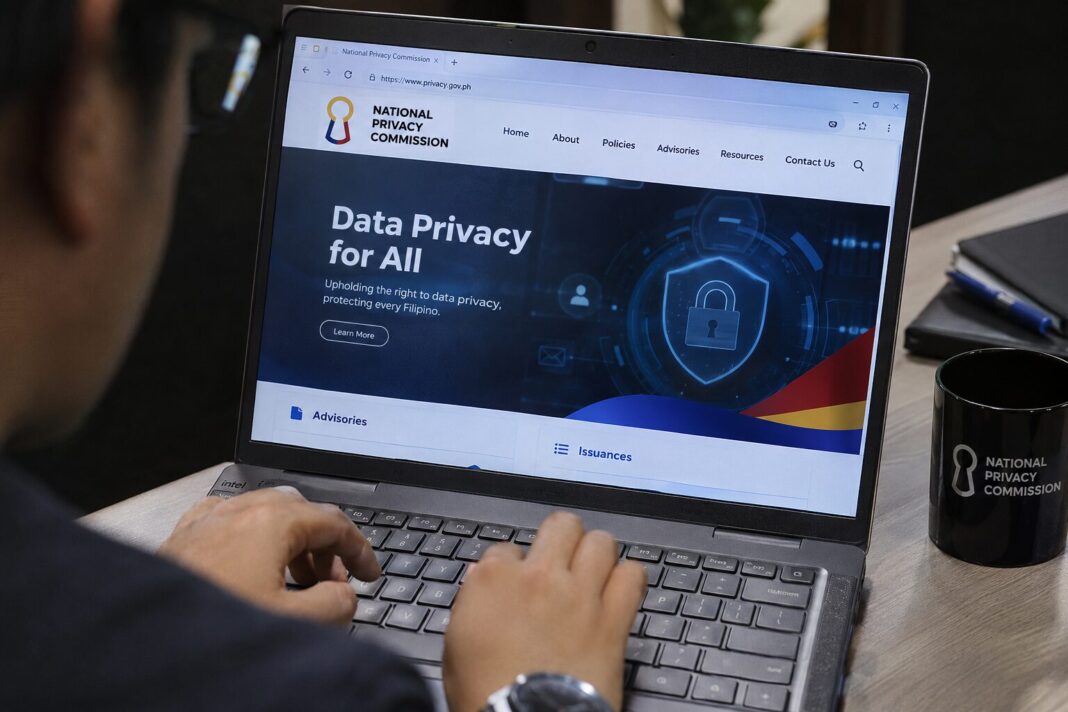
The National Privacy Commission (NPC) has confirmed receiving personal data breach notifications from 10 government agencies, including the Bureau of Internal Revenue (BIR), Securities and Exchange Commission (SEC), and Department of Information and Communications Technology (DICT), amid growing concerns over the security of government-held information.
In a statement issued Tuesday, Nov. 10, the privacy regulator said the notifications also came from the Presidential Commission on Good Government (PCGG), Department of Labor and Employment (DOLE) through its Bureau of Local Employment, and Philippine Amusement and Gaming Corporation (Pagcor).
Other agencies that submitted notifications were the Department of Justice (DOJ) through its Office for Alternative Dispute Resolution, Philippine Coast Guard (PCG), Department of Trade and Industry (DTI), and Department of Science and Technology (DOST) through the Philippine Institute of Volcanology and Seismology (Phivolcs).
The NPC did not disclose the number of individuals potentially affected, the types of personal information involved, or whether the reported incidents were connected.
It also did not provide details on when the incidents occurred or the circumstances surrounding the reported breaches.
NPC deputy privacy commissioner and spokesperson Jose S. Belarmino II said the notifications are being assessed under the Data Privacy Act of 2012 and NPC Circular No. 16-03, which governs personal data breach management.
“The submission of personal data breach notifications is a regulatory requirement under NPC Circular No. 16-03, or the Personal Data Breach Management Circular, for incidents that meet the prescribed notification criteria,” Belarmino explained.
“Each notification received by the NPC is reviewed and assessed by our Compliance and Monitoring Division, which examines the nature and circumstances of the reported incident, its potential impact on affected individuals, and the measures undertaken by the agency concerned. Following its assessment, the Division prepares a report containing its findings and recommendations for submission to the Commission En Banc, which determines the appropriate action or decision based on the circumstances of each case.”
The NPC said submitting a breach notification does not absolve government agencies of their responsibility to address security vulnerabilities and protect individuals whose personal information may have been compromised.
Agencies are required to implement appropriate measures to contain security incidents, minimize potential harm, and prevent similar breaches from occurring.
They must also notify affected individuals when the conditions for mandatory notification under NPC regulations are met.
“Breach notification is only one part of an agency’s responsibility under the Data Privacy Act. Equally important is how the agency responds to the incident, protects the individuals who may be affected, and addresses the vulnerabilities that may have contributed to the breach,” Belarmino stressed.
“Where the prescribed conditions for mandatory notification are met, affected data subjects must also be notified in accordance with the requirements and timelines set under the Circular. The NPC expects government agencies to demonstrate accountability not merely through compliance with notification requirements, but through concrete and effective measures to safeguard personal data and prevent similar incidents from recurring.”
The commission also clarified that government agencies remain responsible for protecting personal information even when data processing operations are outsourced to private contractors or third-party service providers.
Under Section 21 of Republic Act No. 10173, government agencies acting as personal information controllers retain accountability for data under their control or custody, including information transferred to external service providers.
The NPC said outsourcing arrangements do not remove an agency’s obligation to maintain appropriate organizational, physical, and technical safeguards.
These responsibilities include establishing incident response mechanisms, promptly addressing security incidents, and complying with breach notification requirements.
Meanwhile, the commission warned the public about possible phishing attempts, fraudulent messages, identity theft, and other social engineering schemes that could exploit concerns surrounding the reported government data breaches.
It advised individuals to avoid suspicious links and attachments, exercise caution when responding to unsolicited communications, and refrain from disclosing personal or sensitive information to unverified parties.
The NPC said it continues to monitor the reported incidents and will determine appropriate regulatory actions based on the findings of its assessments.