A transport-sector coalition has called on the Department of Transportation (DOTr) and the Land Transportation Franchising and Regulatory Board (LTFRB) to issue a technical report on two alleged cybersecurity incidents, including one that purportedly exposed 16 million records.
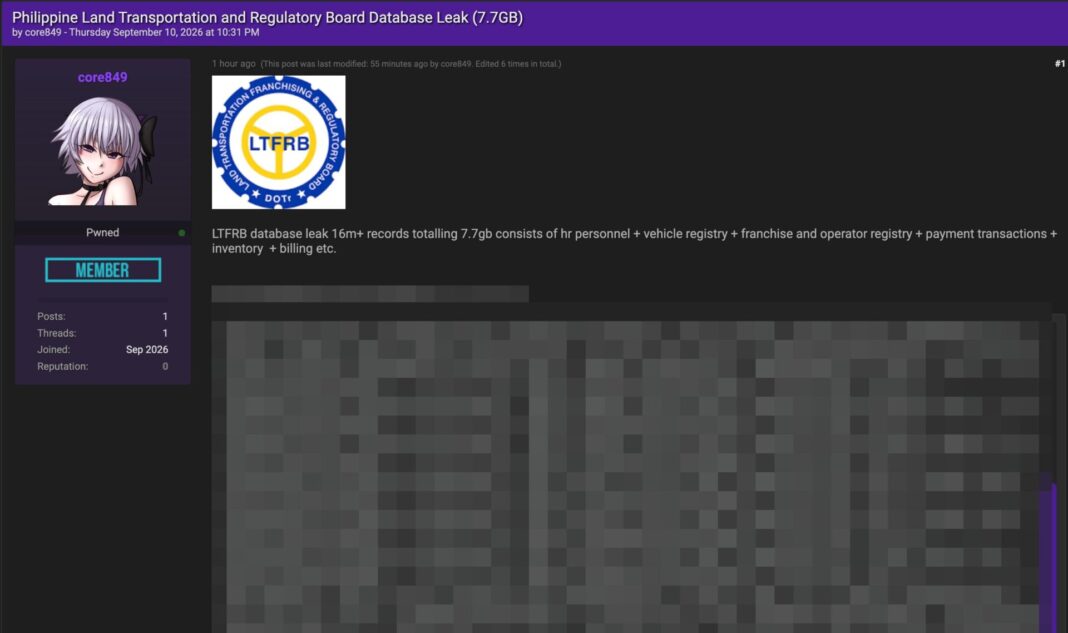
A report by cybersecurity news site Deep Web Konek said a threat actor using the name “core849” claimed to have obtained 7.7 gigabytes of data from the LTFRB.
The allegedly compromised information included personnel records, vehicle registration data, and franchise and operator records, according to the report published on Sept. 12.
Neither the reported intrusion nor the authenticity and provenance of the purportedly exposed data have been independently confirmed.
Coalition 169 said the latest claim followed another alleged incident in August involving a group calling itself “Quantum Security Group.”
“At this stage, it has not been independently confirmed whether unauthorized access to or acquisition of data occurred. Details remain unclear,” the coalition said.
It said the lack of a detailed public technical update from the DOTr and LTFRB was contributing to uncertainty about whether government systems or personal information had been compromised.
“If the reports are unfounded, a clear statement supported by technical findings would put the matter to rest. If the incidents remain under review, the public should be informed of the steps being taken and when the findings are expected,” the group said.
Coalition 169 asked whether the Cybercrime Investigation and Coordinating Center or another independent authority had been directed to verify the claims. It also sought information on the systems reviewed and whether the National Privacy Commission had been notified.
Under the Data Privacy Act, organizations are required to notify the privacy commission and affected individuals of a personal data breach when the incident is likely to create a real risk of serious harm, subject to the conditions prescribed by privacy regulations.
The coalition cited its previous effort to obtain information on government approvals issued after 2013 for the Stradcom-operated information technology system of the Land Transportation Office.
“We recall our prior experience seeking clarification on post-2013 approvals relating to the Stradcom-operated LTO IT system, where clarification was ultimately obtained through the Department of Economy, Planning and Development, formerly the National Economic and Development Authority. We hope similar third-party recourse will not be necessary here,” it said.
Coalition 169 stressed that it was not claiming a breach had taken place but was seeking an authoritative account from the agencies involved.
“Silence breeds uncertainty. Uncertainty erodes trust. Trust is essential when government agencies hold the personal information of millions of Filipinos,” it said.
“The public is not asking for speculation. It is asking for a prompt, factual, and authoritative account directly from the agencies entrusted with protecting its data.”